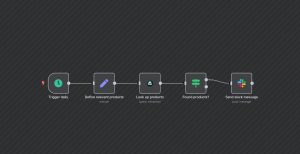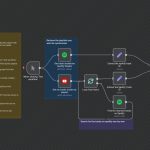
This n8n workflow automates the monitoring of logs to detect suspicious activity, specifically focusing on failed login attempts. The process begins with a scheduled trigger, which triggers an API request to fetch recent logs from an external logging service. It then filters and counts failed login events, comparing the count against a threshold (e.g., more than 5 failed attempts). If exceeded, it sends an alert message with detailed information via Slack to notify your security team of potential threats. This automation provides a practical approach for IT and security teams to proactively identify and respond to potential cyberattacks such as brute-force login attempts. Its ease of setup and targeted alerts make it ideal for improving security oversight without complex SIEM implementations.
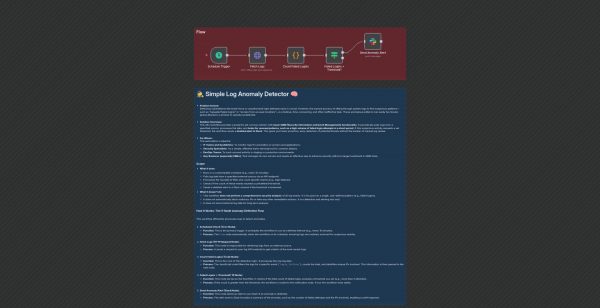
Automated Log Anomaly Detection with Slack Alerts
| Node Count | 6 – 10 Nodes |
|---|---|
| Nodes Used | code, httpRequest, if, scheduleTrigger, slack, stickyNote |