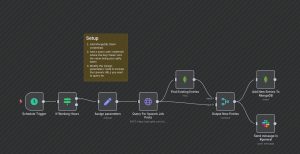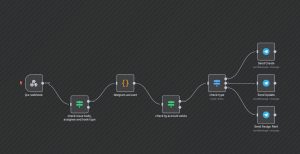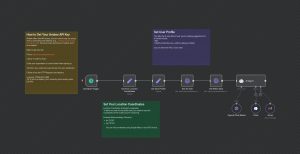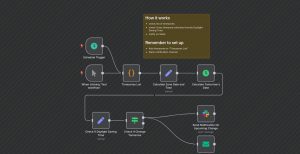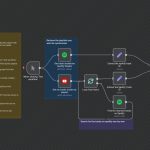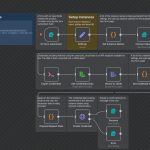
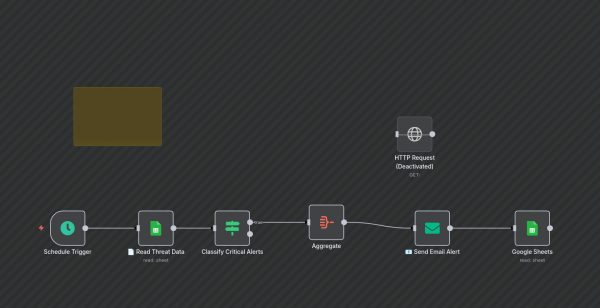
This n8n workflow automates the process of monitoring threat data, classifying critical alerts, and sending email notifications. It starts with a scheduled trigger that initiates the workflow, reads threat data from Google Sheets, classifies alerts as critical or non-critical, and finally sends email alerts when needed. The data is also stored or logged in Google Sheets for record-keeping. This setup is ideal for security teams or IT administrators who need real-time alerting and efficient management of threat information. The workflow can be customized to fit various security or monitoring scenarios, ensuring prompt reactions to potential threats.
Automated Threat Alert Response System
| Node Count | 6 – 10 Nodes |
|---|---|
| Nodes Used | aggregate, emailSend, googleSheets, httpRequest, if, scheduleTrigger, stickyNote |